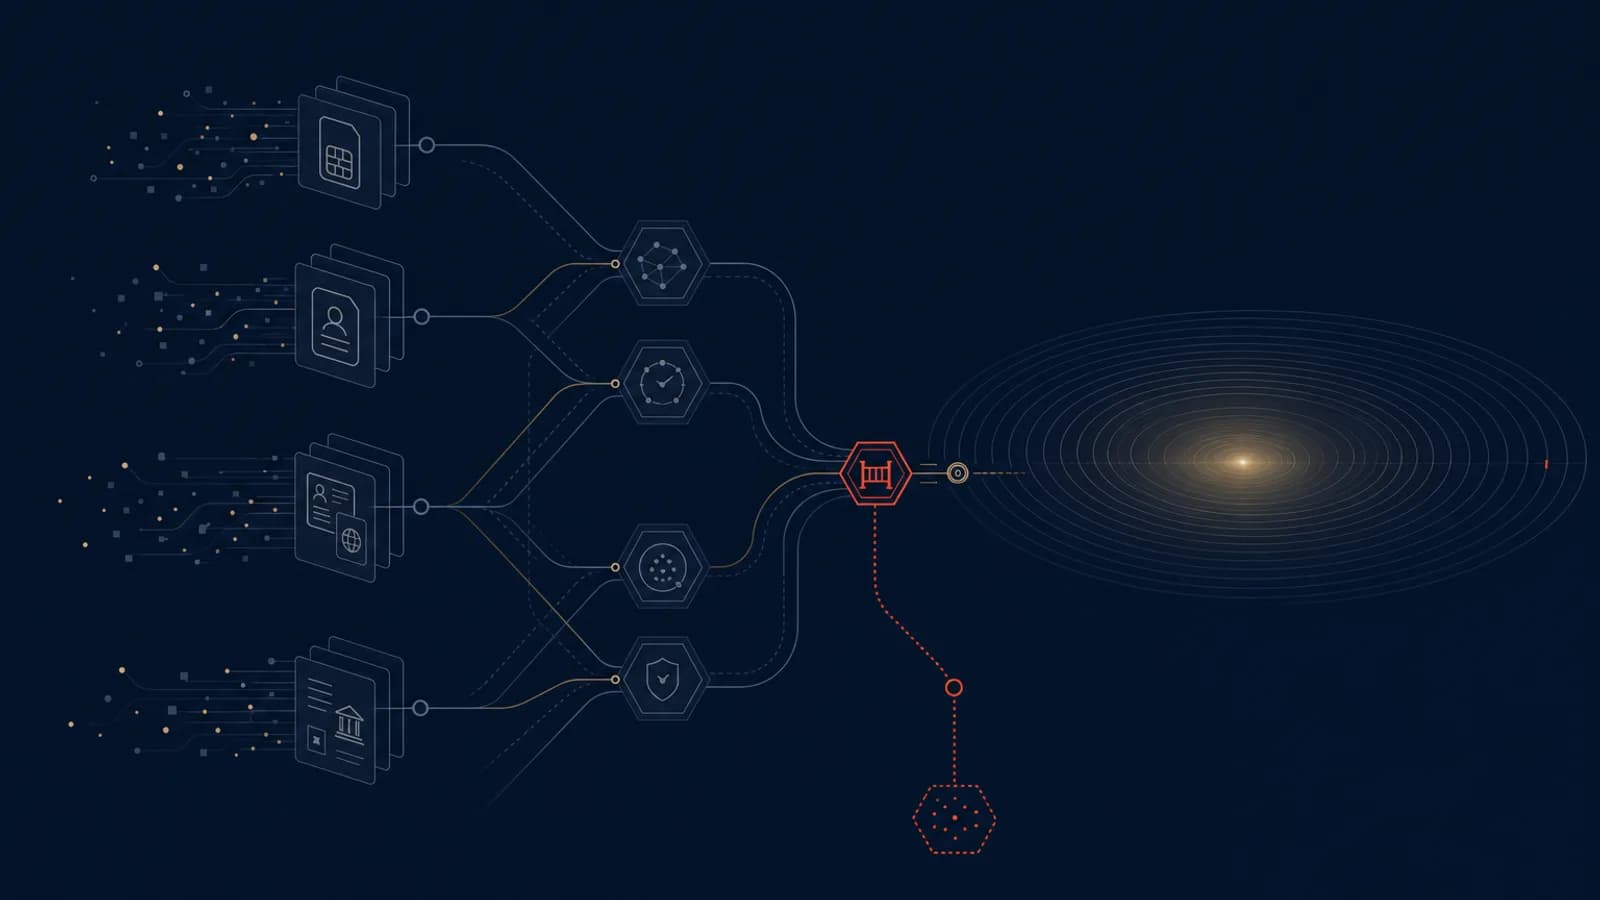
At a Tier-2 MNO, Southeast Asia, ~18M subscribers, the wholesale team faced a familiar post-launch question: which party could produce the identity trail for prepaid SIMs activated through an MVNO’s retail estate. The contract assigned customer onboarding broadly; the evidence sat across three systems. The immediate issue was not screening volume but the ownership of SIM registration from capture through retention, remediation and regulator access.
The launch model concealed a split in accountability
The operating model looked coherent at launch. The MNO retained numbering, IMSI allocation and network-facing subscriber activation. The MVNO appointed and managed point-of-sale agents, captured identity documents and handled most customer communications. Each party could point to a defined activity. Neither had been named as owner of the complete subscriber record, including the evidence supporting the final activation decision.
That distinction became material only when the audit request arrived. The wholesale agreement said the MVNO would perform KYC. It did not state whether this meant collecting documents, validating them, screening the subscriber, resolving exceptions or retaining evidence for the statutory period. More importantly, the wording did not alter the MNO’s licence conditions. SIM-registration obligations and regulator-facing duties often remain attached to the licensed operator even when retail execution is delegated.
Task ownership therefore had to be separated from legal accountability. Retail registration sat with the MVNO’s agents. Identity-document validation was performed by an external vendor. Sanctions and PEP screening ran through a second service. Beneficial-owner checks applied only to certain business accounts. Suspicious-activity escalation moved between the MVNO compliance team and the MNO’s regulatory function. The contract described these activities, but it did not establish who could close an unresolved match, approve an override or accept the residual risk.
The decisive control was activation. The parties had not documented which system held authority to stop an ICCID/IMSI pair from becoming serviceable when the KYC state was incomplete, expired or under review. The MVNO front end submitted an activation request after document capture. The MVNE workflow checked mandatory fields. The MNO’s BSS/OSS provisioned service after receiving a valid transaction. None of those controls, by itself, established that the underlying identity decision was complete.
In the anchor case, the MVNO produced document images and agent declarations. The MNO produced activation timestamps and provisioning records. The identity vendor could confirm that checks had run, but its retained response data did not show the full match disposition. No party could assemble a complete, immutable sequence linking source evidence, screening results, exception handling and the decision to activate. An apparently settled launch had become a contested compliance liability.
“The regulator does not ask which system created the record; it asks who can prove why the subscriber was activated,” a Tier-2 head of wholesale recently observed.
A defensible model follows the subscriber lifecycle
The broader implication is that compliance allocation should follow the subscriber lifecycle, not the system boundary. The control map starts before activation, with data collection, identity assurance and screening. It continues through periodic refresh, event-driven review, suspension, MNP, disconnection, number recycling and statutory retention. A hand-off between platforms does not end accountability for the decision made at that stage.
Each decision that changes subscriber eligibility needs one named control owner. Execution may remain distributed across an MVNO front end, MVNE workflow, identity vendor and MNO provisioning stack. Decision rights should not be distributed in the same way. One party must own the acceptance criteria, exception policy, override authority and evidence standard. The governance model should also state who can suspend service when a control fails after activation, and within what period.
A Greenfield MVNO, post-2023, multi-IMSI stack, applied this approach after finding that its initial design captured the required data fields but not the basis of the eligibility decision. The revised record included source-document images, verification and liveness results, agent identifiers, consent and disclosure records, screening timestamps, match disposition, override rationale and a tamper-evident activation log. The change did not add another screening layer. It made the existing controls reconstructable.
Evidence custody and data access require separate treatment. The MNO needs timely, regulator-ready access to records relevant to its licence obligations. The MVNO needs enough visibility to remediate failed checks, manage agents and challenge false positives. Neither requirement justifies unrestricted replication of sensitive identity data. Access can be role-based, logged and time-limited, provided the wholesale agreement preserves retrieval rights when a vendor contract ends or a platform is replaced.
MNP is a common source of false assurance. A port-in transfers a service relationship and an MSISDN, but it does not automatically establish that the receiving operator may rely on identity evidence collected elsewhere. Reliance depends on the jurisdiction, the porting process and the evidence available. Number recycling creates the opposite problem: historical records must remain available for the retention period while being clearly separated from the new subscriber’s identity and activity.
The lifecycle model also changes wholesale governance. Monthly operational reviews should cover sample testing, exception thresholds, remediation deadlines, breach notification and agent-quality metrics. Persistent failures should trigger defined escalation, not a general commitment to cooperate. Controls should be tested against actual subscriber files, including dormant accounts, suspended lines, port-ins and records created through agents with elevated rejection or override rates.
Audit readiness is an operating capability
The final test is whether the parties can respond under regulatory time pressure. A production notice rarely arrives in the format anticipated by the system design. It may request all evidence for one subscriber, every activation approved by a specific agent, or the exception population for a defined period. The response process must cross commercial, compliance and technical boundaries without beginning a fresh negotiation over data ownership.
Wholesale schedules should set production-notice service levels by request type and urgency. They should identify the team authorised to receive a notice, the clock that starts the response period and the party responsible for assembling the final file. An acknowledgement target is not enough. The agreement needs measurable deadlines for record retrieval, legal review, exception explanation and secure delivery, with an escalation route that reaches accountable executives before a statutory deadline is missed.
Immutable decision records are central to that process. A useful record shows what evidence was available at the decision time, which rules were applied, which version of the workflow ran and whether a human overrode the result. Subsequent remediation should append a new event rather than overwrite the original state. Without that sequence, an operator may prove that a subscriber is compliant today while remaining unable to explain why service was permitted six months earlier.
Vendor access is another recurring weakness. Identity and screening providers may retain detailed responses in their own environments, subject to separate retention periods and retrieval charges. The operator model should preserve audit access, export rights and continuity provisions through termination, insolvency and platform migration. It should also test whether vendor reference IDs can be resolved in bulk. A reference that works only through a manual support request is not a dependable control for a large exception population.
Exception populations deserve the same discipline as individual subscriber files. Management should be able to identify incomplete registrations, expired documents, unresolved screening matches, manual overrides, failed refreshes and activations performed during system degradation. Threshold breaches need named escalation owners and defined treatment, including suspension where required. Aggregate counts alone are insufficient; each population must reconcile to subscriber-level records and subsequent remediation outcomes.
The practical exercise is straightforward: select a real activation, impose a short regulatory deadline and require the operating parties to produce the complete decision trail without informal intervention. Repeat the test for a port-in, a recycled number and an overridden screening result. The gaps that emerge usually concern authority, access and evidence continuity rather than missing policy language.
As SIM-registration mandates and financial-crime scrutiny tighten, the commercial advantage will sit with MVNO operating models that make control ownership and evidence retrieval routine rather than contractual afterthoughts. MNOs and MVNEs should test the model against a real audit request before subscriber volumes make remediation expensive.